
Securing your VPS: the first five minutes
A new server on the internet gets scanned within minutes by bots trying passwords. These steps keep you well ahead of them. Run them as root.
1. Update everything and turn on automatic updates
- Ubuntu and Debian:
apt update && apt upgrade -y, thenapt install -y unattended-upgradesanddpkg-reconfigure -plow unattended-upgrades. - AlmaLinux and Rocky Linux:
dnf upgrade -y, thendnf install -y dnf-automaticandsystemctl enable --now dnf-automatic-install.timer.
2. Log in with a key, passwords off
First put your SSH key on the server (see Logging in to your VPS with SSH) and test that logging in with the key works. Then create your own settings file /etc/ssh/sshd_config.d/00-eigen.conf with these lines:
PasswordAuthentication no
KbdInteractiveAuthentication no
Don't put it in /etc/ssh/sshd_config itself: the files in sshd_config.d take precedence, and on Ubuntu 50-cloud-init.conf turns passwords back on there. Your 00-eigen.conf comes before it and wins. Check with sshd -t (says nothing if it's correct) and sshd -T | grep -i passwordauthentication (should show no). Then restart SSH with systemctl restart ssh (AlmaLinux and Rocky: systemctl restart sshd). Keep your current session open until you've checked in a second window that you can still get in.
3. A firewall
- Ubuntu and Debian:
apt install -y ufw, thenufw allow OpenSSH, optionallyufw allow 80,443/tcpfor a website, andufw enable. - AlmaLinux and Rocky Linux: firewalld is already installed. For example
firewall-cmd --permanent --add-service=http --add-service=httpsandfirewall-cmd --reload.
Always keep SSH (port 22) open, or you'll lock yourself out.
4. Fail2ban against guessing attempts
apt install -y fail2ban or dnf install -y epel-release && dnf install -y fail2ban, then systemctl enable --now fail2ban. By default it blocks IP addresses that try a wrong password too often. On Debian 12, also set backend = systemd under [sshd] in /etc/fail2ban/jail.local and install python3-systemd, otherwise SSH monitoring won't start. Debian 13 and Ubuntu do this automatically.
5. A snapshot as a safety net
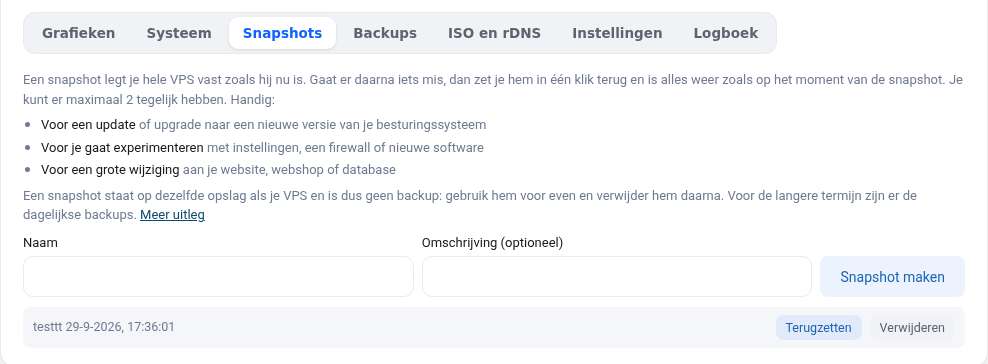
Create a snapshot in your VPS screen before making major changes. If something goes wrong, you restore it in one click. See Snapshots and backups of your VPS.
Leave the qemu-guest-agent in place
The qemu-guest-agent program is installed by default. It lets you set a new root password in the VPS screen and shows you the disk usage. Don't remove it.
Detailed explanation with screenshots: Disabling password login and root login and fail2ban against guessing attempts in the VPS manual.
Want to learn more? Take the free course VPS and Linux server management, lesson 2.2 Setting up the SSH server securely or lesson 10.4 Final check: putting your server to the test.